Check rollout risk in under a minute
Best when you are not sure whether the next move should stay self-serve, become a hosted artifact, or jump straight into a paid founder review.
Run MCP calculatorMCP security scanner / local evidence
One local command for a concrete baseline. mcp-scan is MIT licensed, runs against your configuration, and sends no telemetry.
$ npx mcp-scanCaptured with CLI v2.1.0 on 2026-10-10CRITICAL exposed-secret
Exposed GitHub Token in environment variable 'WEATHER_TOKEN'.
↳ Move the secret to a secure environment variable and reference it instead (e.g., ${WEATHER_TOKEN}).
MEDIUM unverified-source
Server 'weather-demo-server' is an unscoped package from an unverified source (typosquatting risk).
↳ Verify the publisher of 'weather-demo-server' on npmjs.com before trusting this server, or ask the maintainer to publish with npm provenance (npm publish --provenance from GitHub Actions or GitLab CI) so mcp-scan can confirm it automatically.
Scanned 1 server across 1 client in 494ms
1 critical 0 high 1 medium 0 low
Captured from a purpose-built synthetic MCP configuration. It does not inspect this page or your machine.
Open-source baseline
Inspect your configuration
No scan runs on this page
17 supported clients and tools
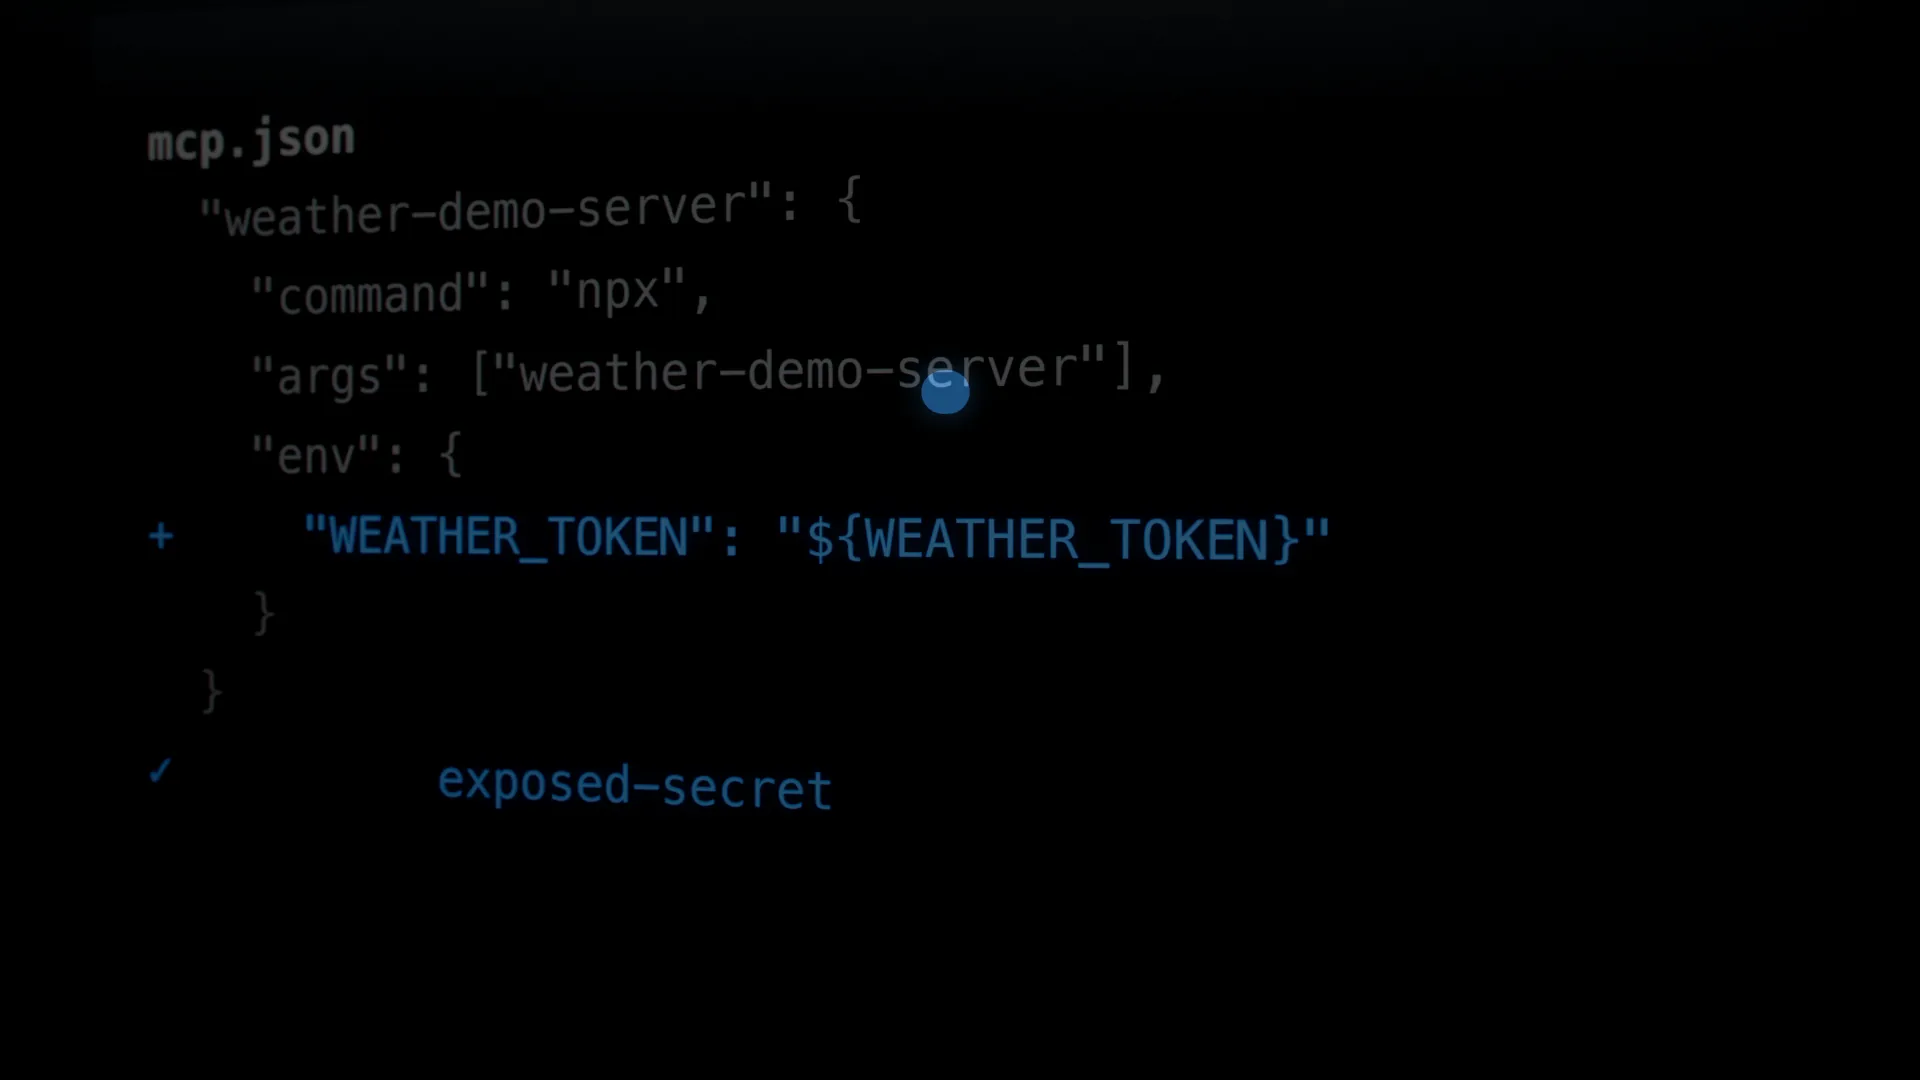
A secret, exposed. One line. Fixed.
Pick the path that matches the decision you need to make before you go deeper.
Best when you are not sure whether the next move should stay self-serve, become a hosted artifact, or jump straight into a paid founder review.
Run MCP calculatorBest when you need a cleaner summary than raw terminal output and want to assess whether a hosted report fits your workflow.
Preview hosted reportBest when rollout is close, permissions are sensitive, and a fast human decision is worth more than reading scanner output alone.
Book MCP reviewA sample of the hosted report: a decision summary, the highest-risk findings, and an export a team can share internally without rewriting raw scanner output by hand.
A shell-capable connector can read local secrets and reach an external host with no approval boundary.
Shortest safe next stepRestrict permissions, pin the server source, and block unrestricted egress before rollout.
The server definition points to a package path that is not pinned to a trustworthy release boundary.
Shortest safe next stepPin the package source and record a known-good version before teammates reuse it.
One tool can receive unconstrained instructions without a clear human-review checkpoint.
Shortest safe next stepAdd a review gate and narrow the tool contract before connecting it to sensitive workflows.
Hosted reports, policy packs, and shareable risk summaries are being explored for teams that need a shareable decision artifact after a local scan. This form is the waitlist, not a purchase.
Best for teams comparing a lightweight hosted report against the human review lane (48 hours from access), where a person verifies whether the current setup is safe enough to ship.
Reserve the narrow lane if the MCP problem is already clear. If the risk is broader than one MCP decision, escalate into a Build Readiness Audit instead of forcing this fixed-scope review. See the full lane details.
mcp-scan provides a unified security layer for the Model Context Protocol ecosystem. Run it locally or integrate with your CI/CD pipeline.
| Scanner module | What it finds | Severity |
|---|---|---|
Secrets Detectionsecret-scanner | Entropy-based scanning for API keys and tokens. | High |
Package Auditpackage-scanner | Audits package manifests and dependency hygiene. | High |
Prompt Injectionprompt-injection-scanner | Analyzes prompts for potential injection vectors. | High |
Tool Poisoningtool-poisoning-scanner | Detects malicious tool definitions and schemas. | High |
Supply Chainsupply-chain-scanner | Verifies the trust chain of connected MCP servers. | Medium |
Data Controlsdata-controls-scanner | Audits PII handling, retention gaps, and privacy control coverage. | Medium |
mcp-scan works across desktop apps, editors, CLIs, and coding tools that expose Model Context Protocol configurations.
Runs in any pipeline with one npx command. Outputs SARIF 2.1.0 for native integration with GitHub Advanced Security and other security dashboards.
- name: MCP Security Scan run: npx mcp-scan@latest --sarif mcp-scan.sarif- name: Upload SARIF uses: github/codeql-action/upload-sarif@v3 with: sarif_file: mcp-scan.sarif
mcp-scan is free, open source, and built for the community. Zero telemetry. No vendor lock-in. The full test suite runs in the public repo on every change.
npm install -g mcp-scannpx mcp-scanFAQ
mcp-scan is an open-source security scanner for Model Context Protocol (MCP) server configurations. It detects leaked secrets, prompt injection risks, supply-chain vulnerabilities, and misconfigurations across 17 supported AI clients and tools, including Claude Desktop, VS Code, Cursor, and Windsurf.
Run `npx mcp-scan@latest` in your terminal. No installation required. It automatically detects and scans all AI tool configurations on your system.
Yes. mcp-scan is completely free and open-source under the MIT license. It has zero telemetry and collects no data.
mcp-scan runs 16 scanners with 17 named finding types across secret detection, prompt injection scanning, supply chain risk analysis, typosquatting detection, data flow analysis, network egress monitoring, and compliance mapping (SOC 2, GDPR, HIPAA).